Technology
Researcher says Telegram Desktop flaw enabled one-click file theft and possible account takeover
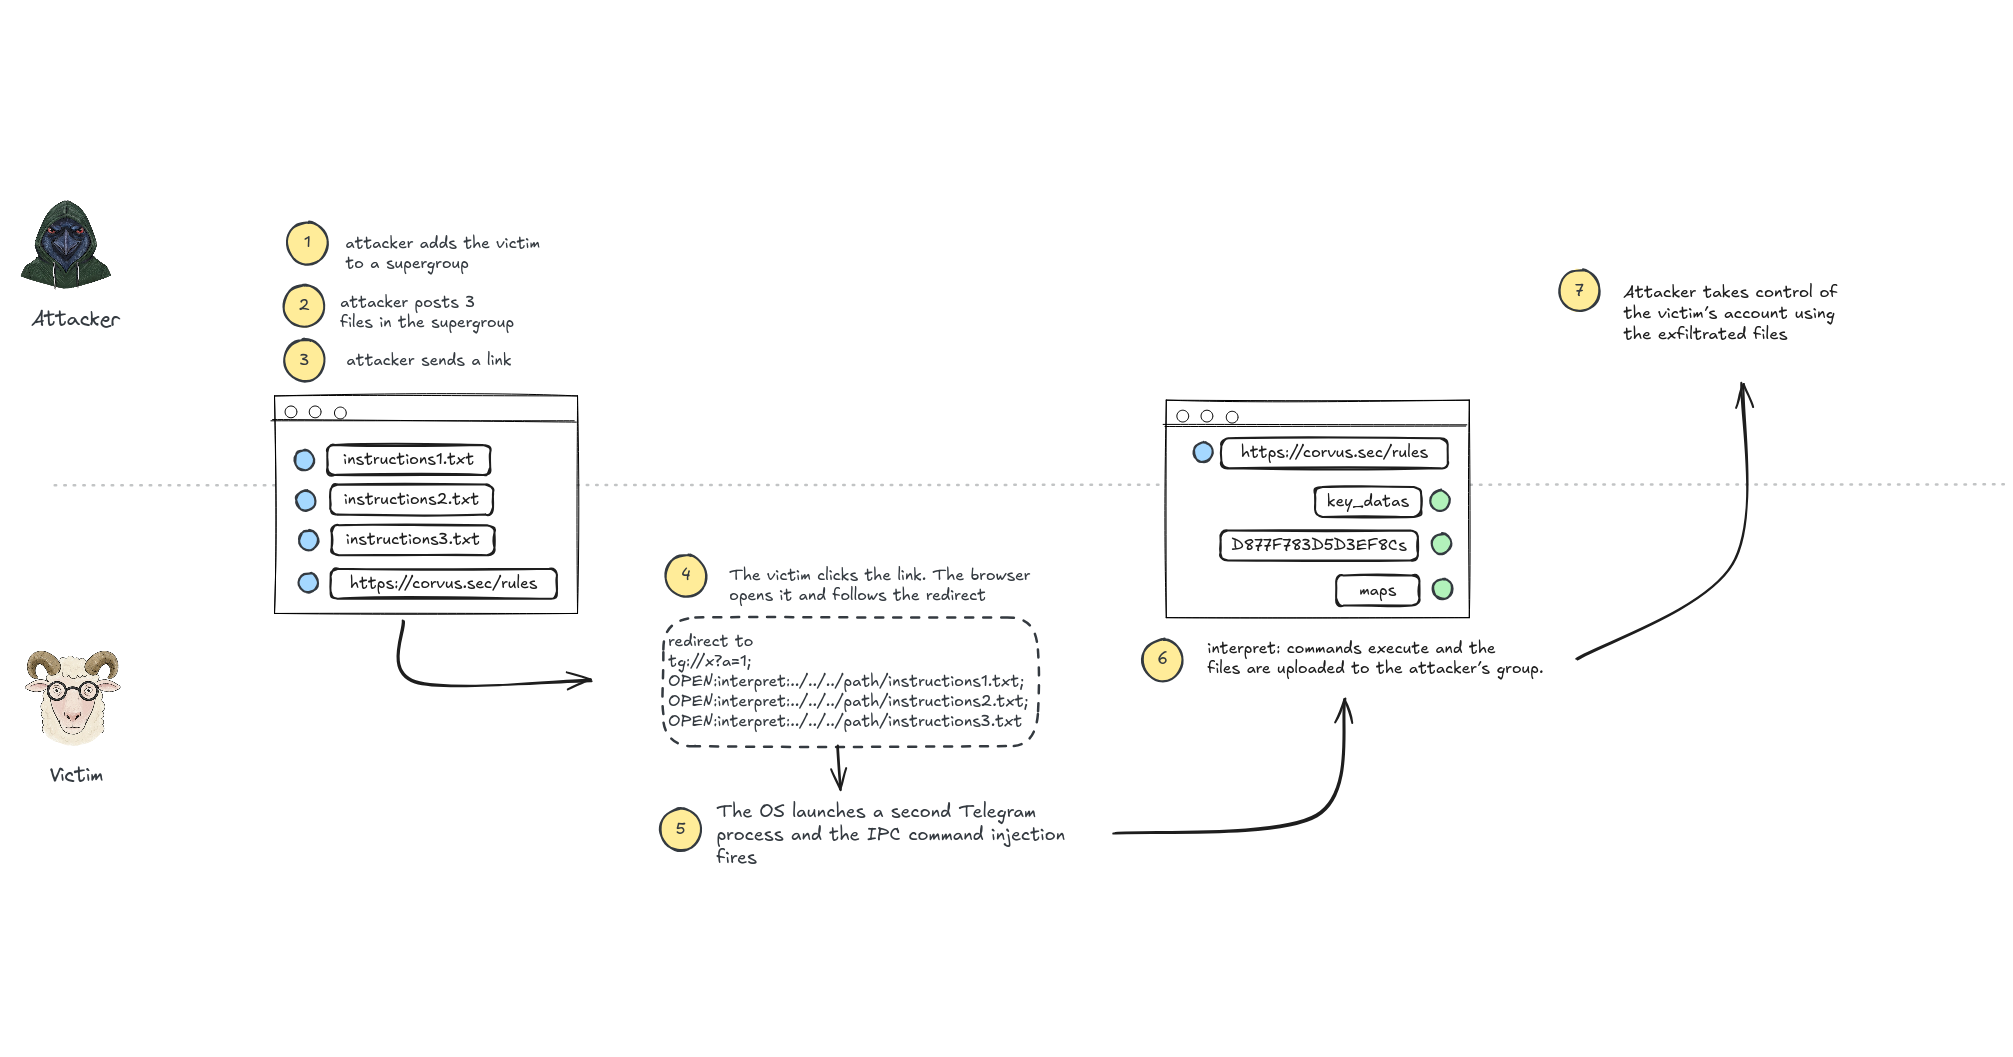
A researcher says a vulnerability in Telegram Desktop’s local link-handling system allowed a crafted external link to inject commands into a running client and reach an internal file-sending function. In the described proof of concept, attackers could place instruction files through automatic group downloads, steal session-related files and reconstruct an account session without confirmation. The researcher says Telegram fixed the chain in version 7.2.9 by removing the legacy scheme, escaping socket separators and adding checks. Users should upgrade; local passcodes reduce exposure but do not prevent file theft.
Editorial summary · Publisher article
What matters
- The exploit combined an unescaped command separator with an internal interpret scheme that lacked authorization checks.
- A group attacker could use automatically downloaded text files to specify files for exfiltration.
- The report says stolen session files could be sufficient to open the victim’s Telegram account elsewhere.
- The fix shipped in version 7.2.9, released after a September 16 commit.
Context & caveats
- The account-takeover scenario depends on the victim clicking an external link and on the described default download behavior.
- The report is an independent technical analysis; the packet does not include a Telegram security advisory.
Why this made the edition
Detailed technical reporting explains a plausible one-click file-theft and account-takeover chain, provides a proof-of-concept sequence, identifies the fix and gives concrete mitigations.
Source material